

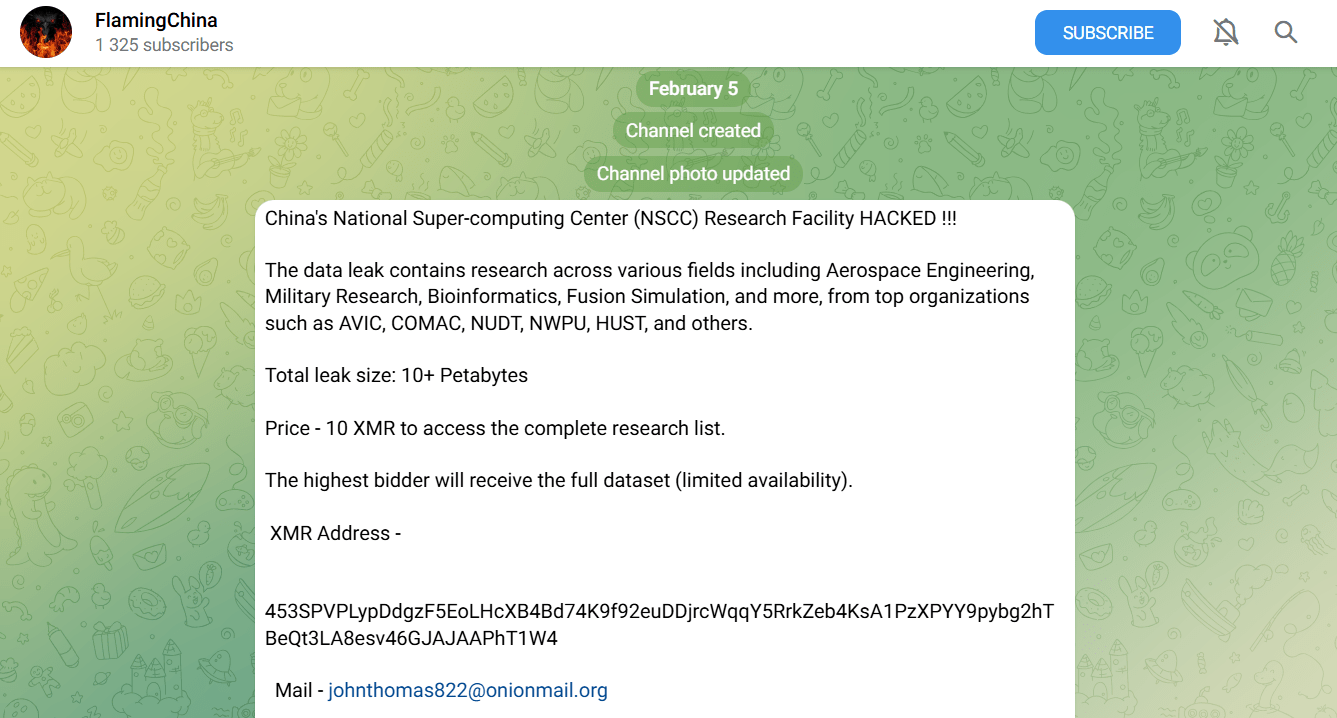
A hacker using the name “FlamingChina” claims to have pulled more than 10 petabytes of data out of China’s National Supercomputing Center in Tianjin, a state-run high performance computing hub that supports thousands of research, industrial, and government users.
Multiple outlets reporting on the leak say the claim is still unverified, but analysts who reviewed sample files told CNN the material looks consistent with the kind of work run through the facility.
The Operation
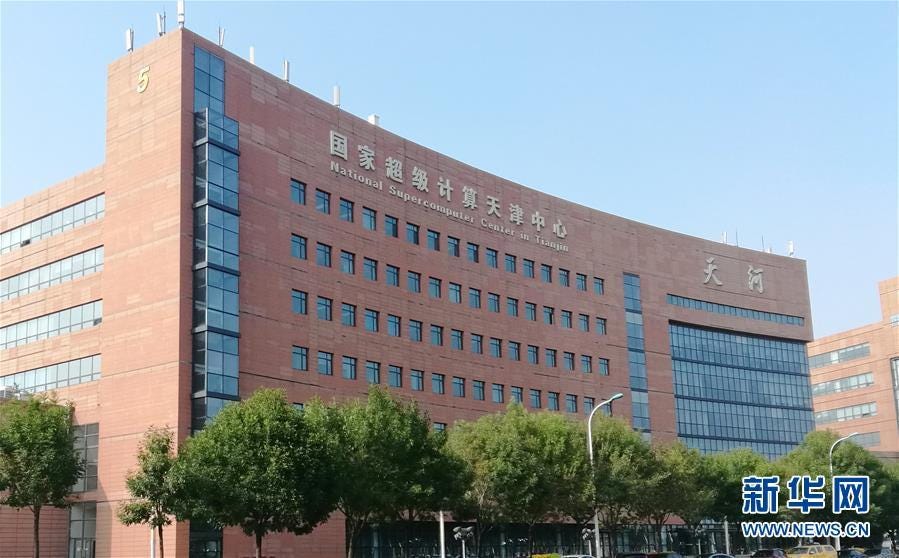
Reporting around the case points to the National Supercomputing Center in Tianjin, often shortened to NSCC-TJ, as the likely source of the stolen material. Official descriptions of the center say it serves roughly 6,000 clients across China, including research institutes, businesses, and government agencies. That client base helps explain why the leaked samples reportedly cut across aviation, weapons work, scientific modeling, and other technically different but compute-heavy disciplines.
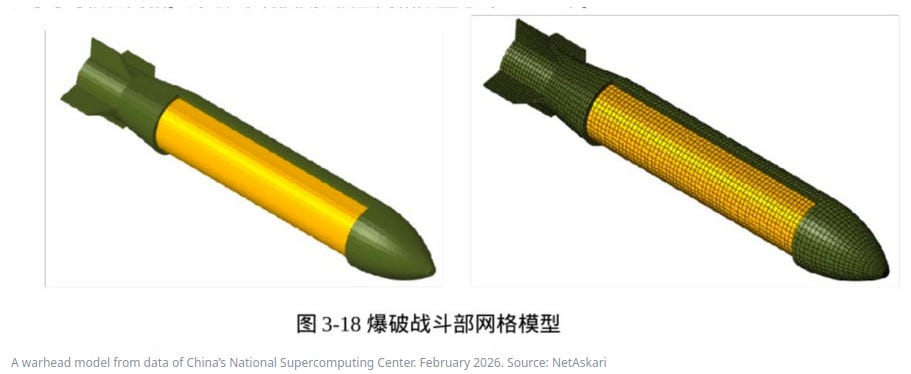
The seller posted the data for sale on February 6, 2026, according to reporting cited by TechRadar and Security Affairs. Limited samples were allegedly offered for smaller amounts, while full access was marketed for hundreds of thousands of dollars in cryptocurrency. Analysts cited in that reporting said the samples included schematics and renderings tied to aircraft, missiles, bombs, and other high-end research outputs.
A supercomputing center brings together computing workloads, stored data, and research outputs from multiple users in one environment.
If that environment is compromised, the exposure may extend beyond final documents to include simulation files, draft models, test results, and other working material. In practice, that can provide a more detailed view of a program’s development than polished public or internal summaries alone.
The Actors
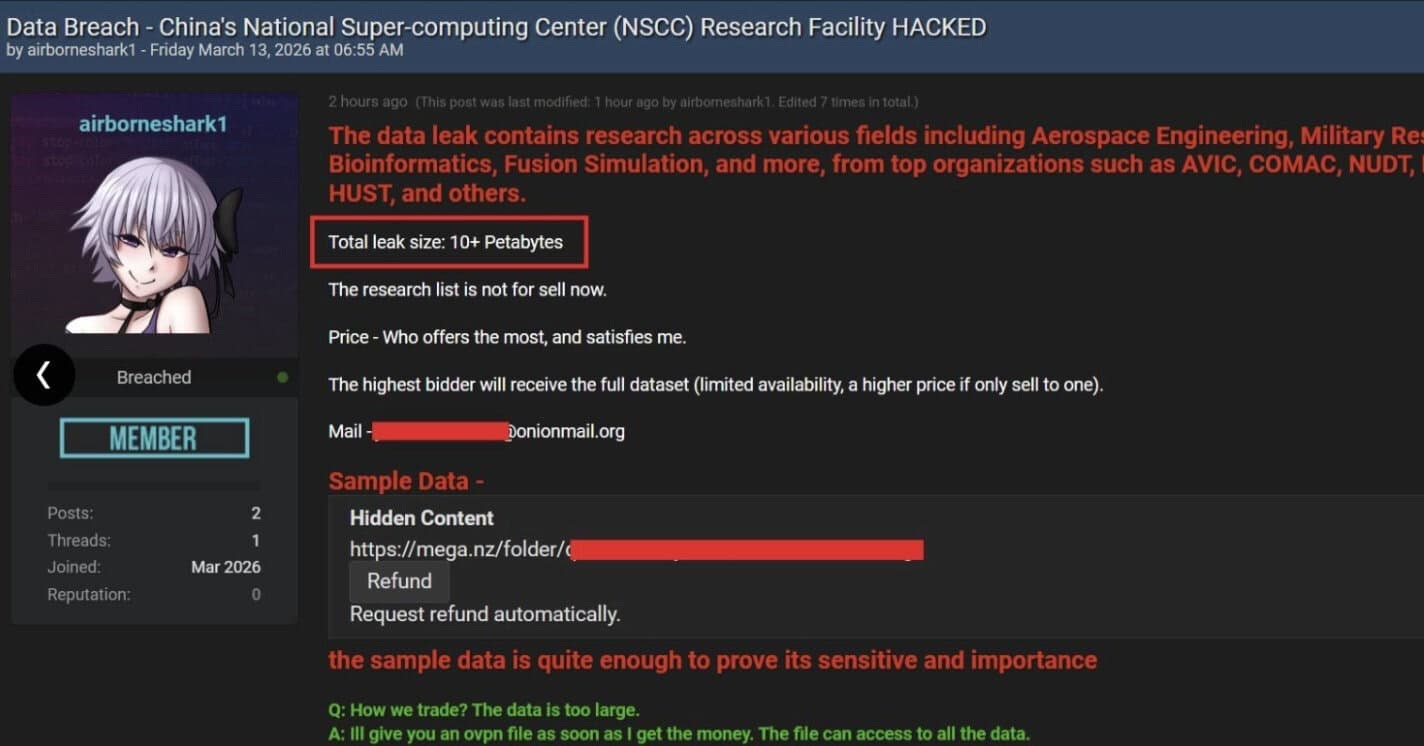
Very little is firmly established about FlamingChina beyond the handle itself. Public reporting does not identify a known crew, a leadership structure, or a confirmed state sponsor. Right now, “FlamingChina” is best understood as the name attached to the sale and leak operation, not a fully attributed threat actor with a proven history. Multiple reports describe it as either a single hacker or a small group, which is another way of saying nobody credible has pinned down the real size of the operation yet.
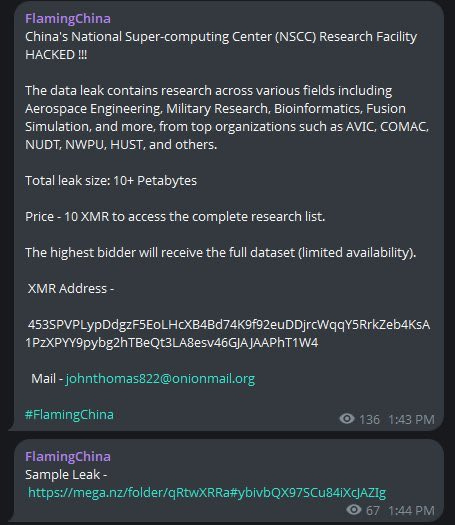
The first public trace appears to be in early February 2026. Reporting says an account calling itself FlamingChina posted sample material from the alleged Tianjin haul on an anonymous Telegram channel on February 6. SpyCloud’s February cybercrime roundup says the same leak was offered for sale on February 4 on a BreachForums successor by a user named airborneshark1, and adds that the actor releasing the data appeared to run the FlamingChina Telegram channel as well. That does not prove FlamingChina is an established group with multiple operators, but it does suggest the persona was active across at least two distribution channels, a forum sales post and a Telegram leak channel.
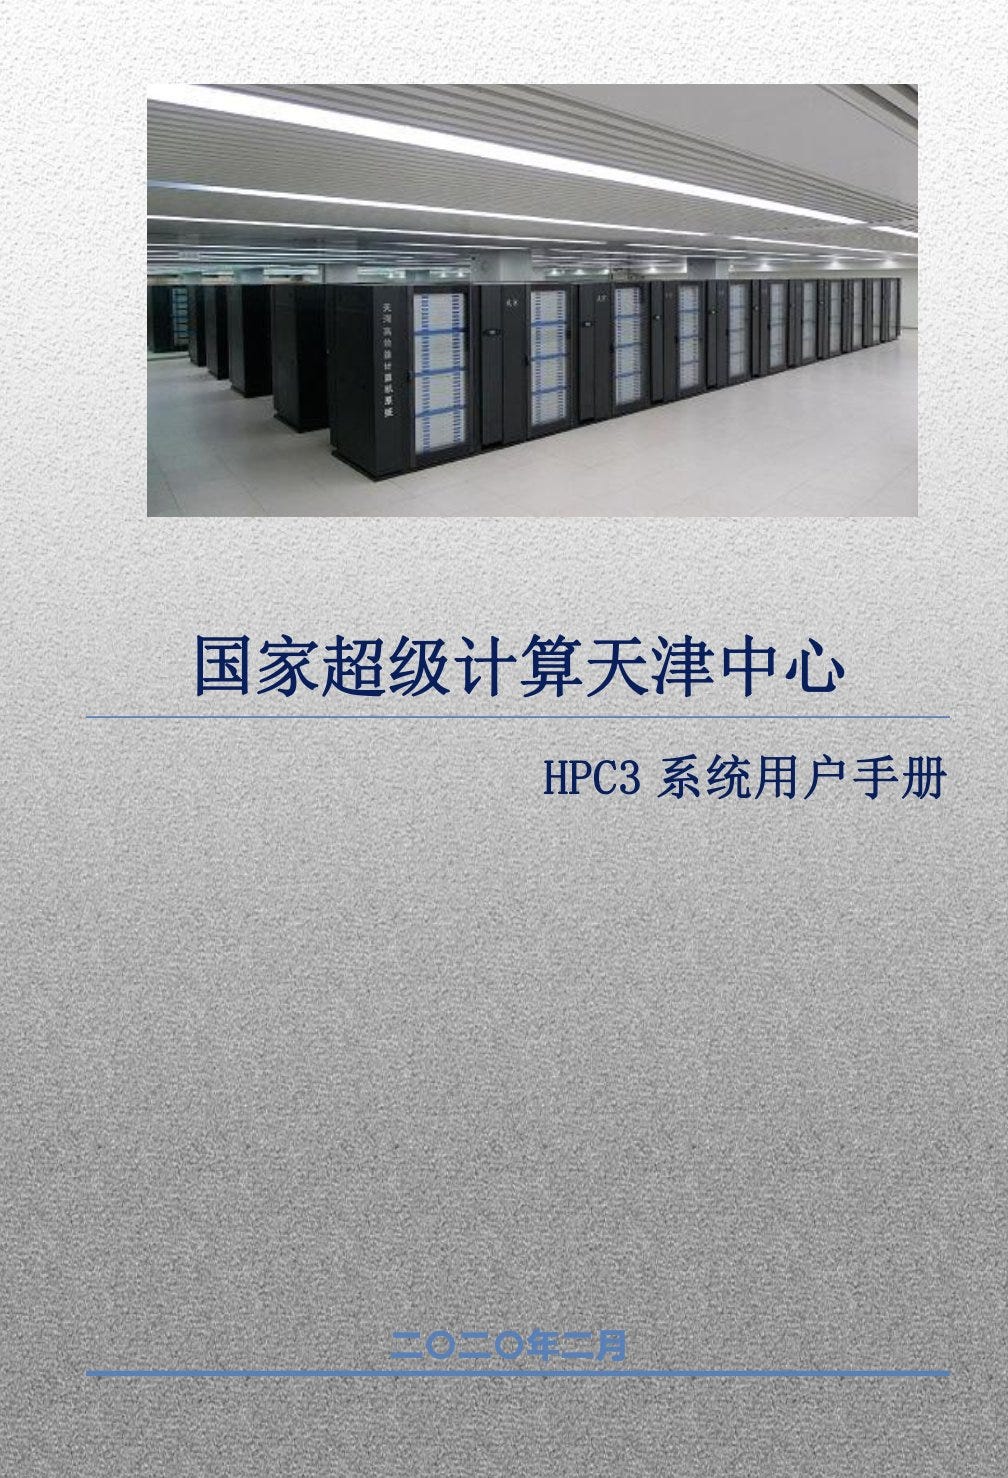
On manpower, there is no reliable public number. No outlet I found gives a confirmed member count, and no threat-intelligence reporting in the public domain ties the name to a known roster, affiliate network, or broader criminal ecosystem.
Location is also unresolved. The target was in Tianjin, but that says nothing about where the operator sat. The infrastructure discussed in reporting, Telegram, crypto payment, breach-market sales, and a claimed botnet-assisted exfiltration route, points to a remote actor with access to standard cybercrime channels, not to a physically proximate penetration team.
Conclusion
If the leak is real, this was not just theft of stored data. It was access to a national-level research and simulation backend that appears to have pooled work from defense, aerospace, science, and government clients in one place.
That is the kind of compromise that lets an adversary map programs, dependencies, timelines, and weak points across sectors at once.